FinregE Governance
Policy management that survives the auditor's question.
FinregE Governance runs every policy, procedure and standard from draft to attestation in one governed workflow, with enterprise search that answers, version control that reconstructs any date, approvals that can’t be skipped, and AI mapping from the regulation to the clause that meets it.
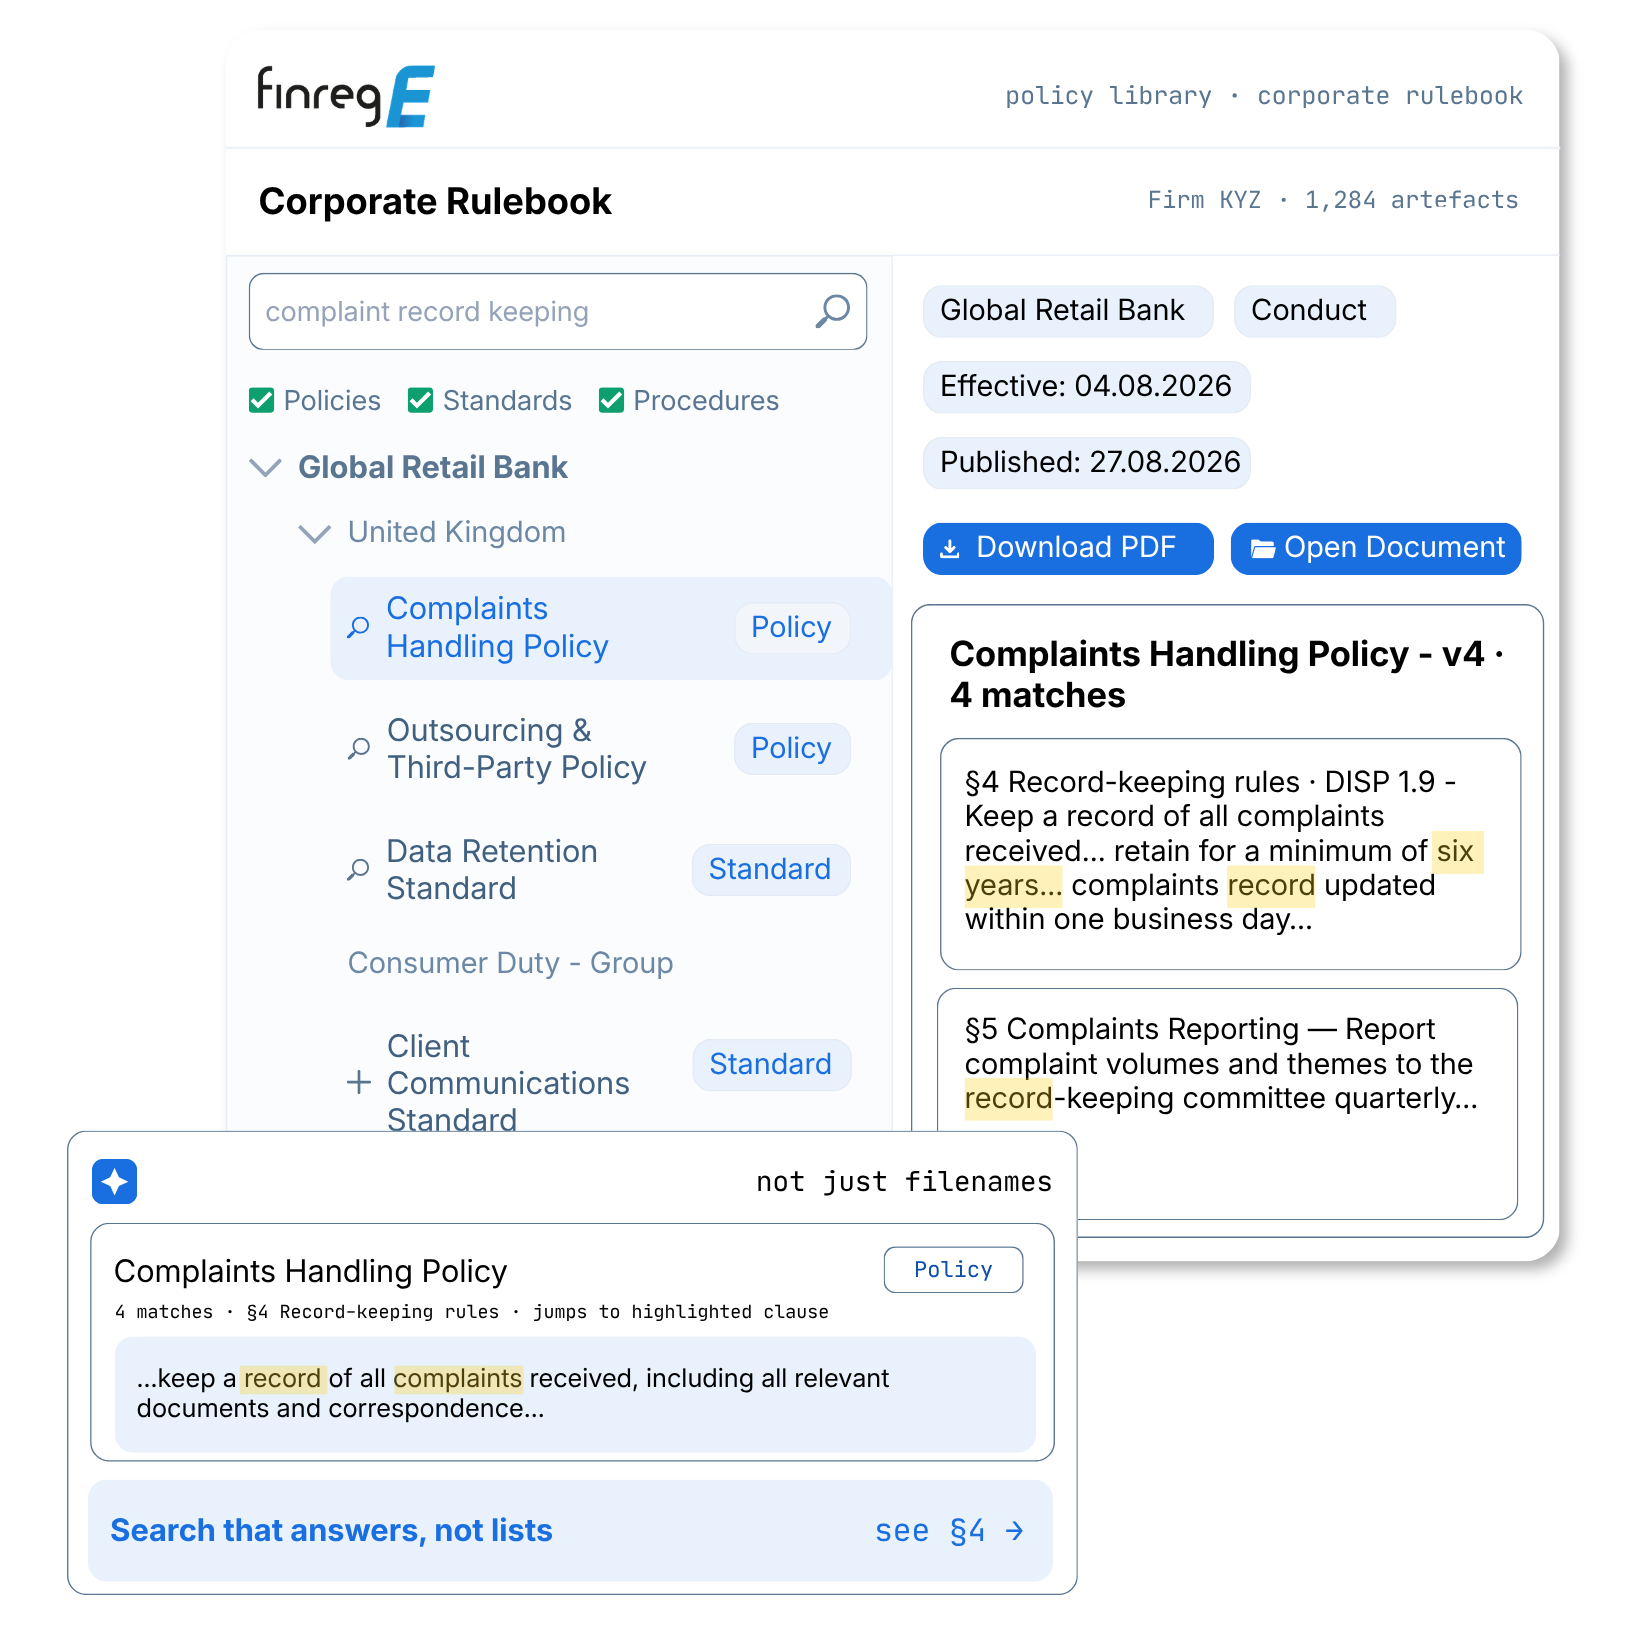
Policies, procedures, standards and controls in one structured store, with a data dictionary.
Q&A answers from your internal documents – cited, permission-aware, and it refuses the unknown.
Drafting with review and approval gates, tracked changes, and role-based permissions.
View any version, compare clause-level changes, roll back with a full audit trail.
Keep obligations mapped to the policies and controls that meet them and gaps flagged.
Policies
Procedures
Standards
Guidance
Playbooks
Risk appetite
Delegations
Committee terms
Forms & templates
Folders hold files. Governance needs evidence.
Most firms run governance on Word drafts, email threads and SharePoint libraries, so the same question gets asked again every month, “final_v7_really_final.docx” decides what the rule actually is, and nobody can show a regulator which version was approved when. Governance moves every artefact into one structured, permission-aware store that an LLM can actually reason over.
Status quo · 1
Word + email drafting
- Version sprawl, no single approved copy
- Tracked changes lost between inboxes
- Who approved what and why, reconstructable only by memory
- No link from a clause to the obligation behind it
Status quo · 2
SharePoint libraries
Better than nothing, but folders rot, copies multiply, and search still only finds filenames.
- Version history is not a governed lifecycle
- Search finds filenames, not the clause that answers the question
- No attestation, no orphan detection, no review-cycle MI
- Generic AI guesses across superseded duplicates
FinregE Governance
One governed source of truth
Structured artefacts, gated approvals, cited answers mapped to the regulation that forces them.
- One approved truth per policy, every version retrievable “as at” any date
- Approval gates replace cc threads; leaver queues bulk-reassigned in one op
- RIG answers “what's our policy on…?” with paragraph citations
- Regulatory change highlights the affected clause before anyone searches
One library the whole firm can search and AI can read.
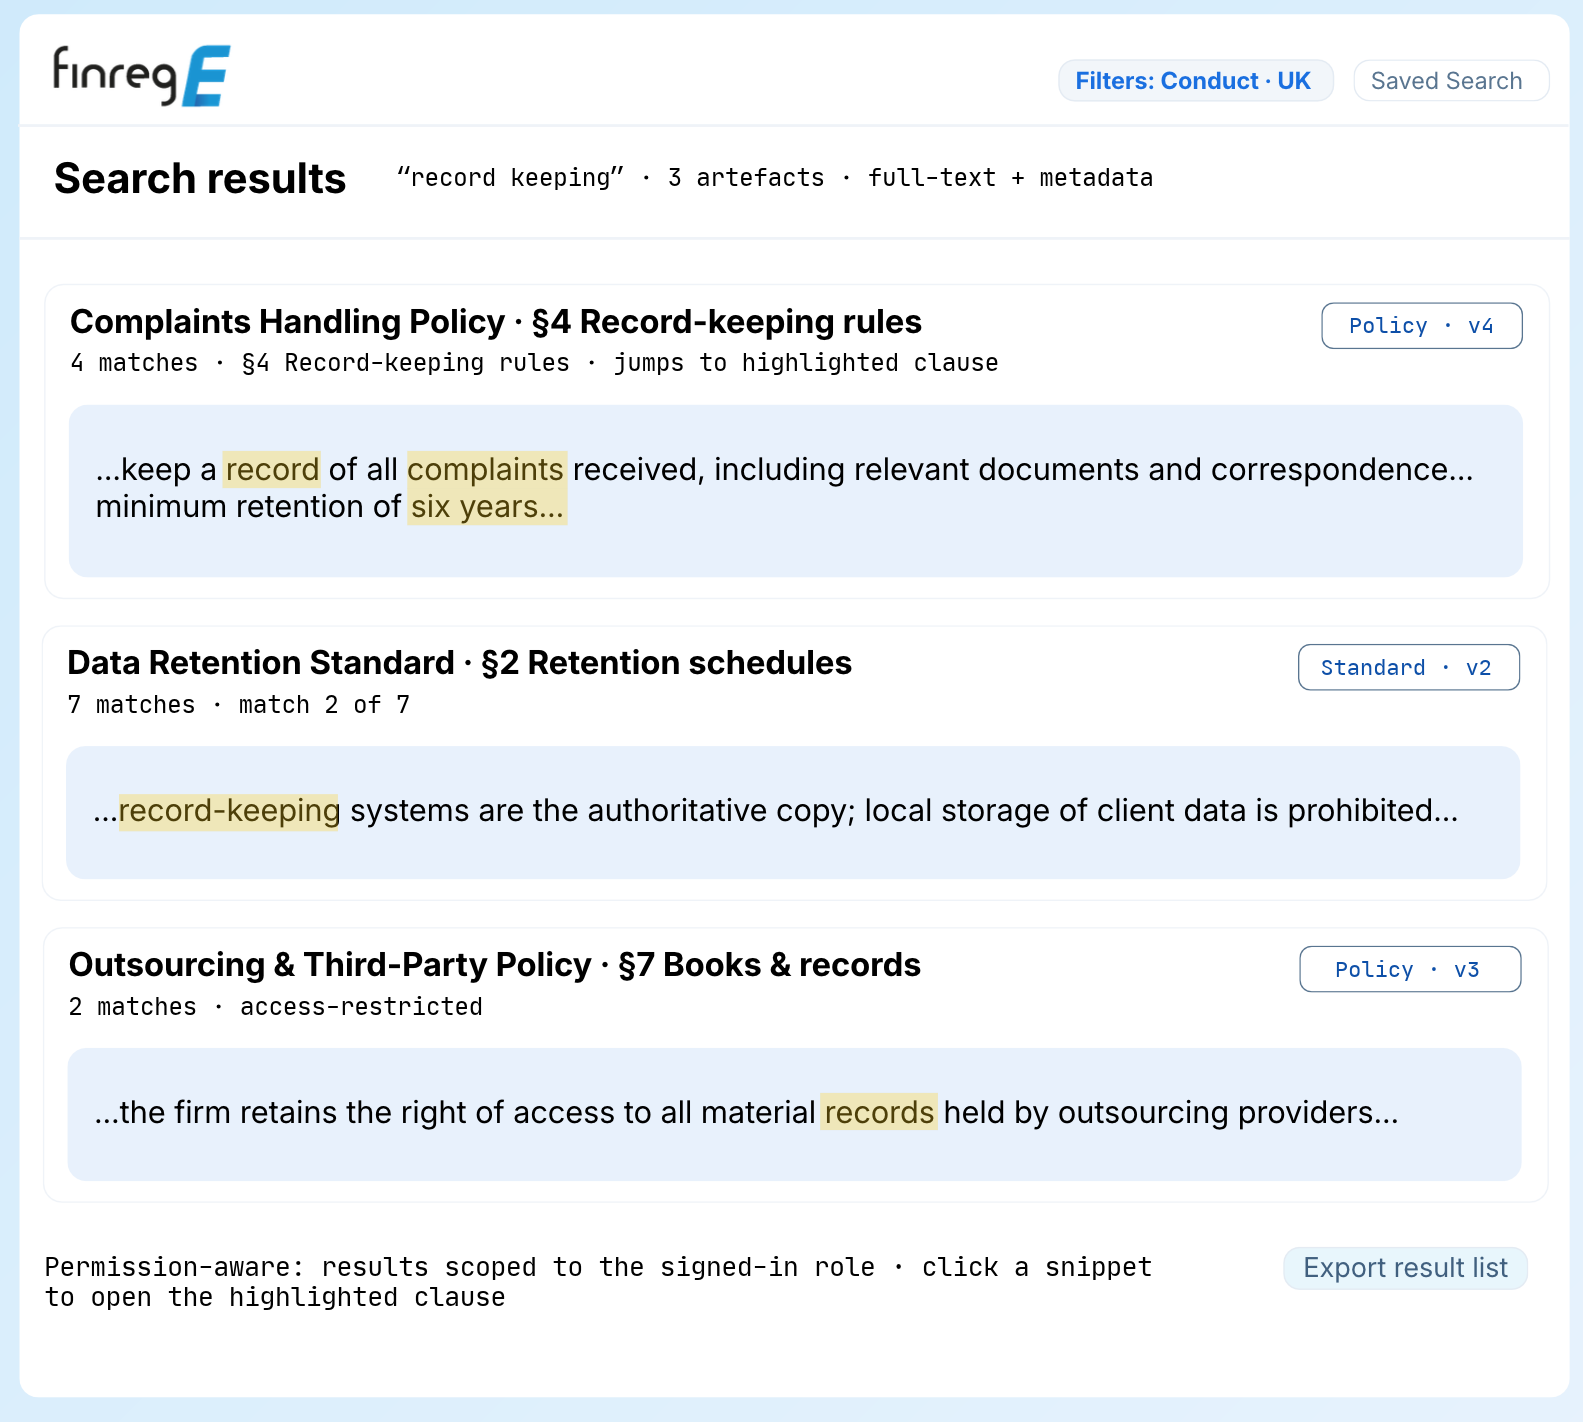
A single enterprise search matches document titles and the full text of every policy, procedure and standard. Results show the exact section or clause, the match count and a keyword-in-context snippet, so people judge relevance before opening, then click straight to the highlighted passage.
- Open access by default, RBAC when you need it: give every employee the whole library, or scope by entity, division or sensitivity, permissions apply to search and AI answers, not just browsing.
- Rich metadata, not filenames: owner, business unit, division, document type, parent document, authorised-by, effective date and custom fields, filterable, exportable and admin-configurable without vendor services.
- Ingest what you have: Word, PDF and Excel load in bulk without reformatting to a template; OCR makes scanned PDFs searchable; tracked-changes checks catch bad conversions on import.
- Links that never break: every version has its own URL, so intranets, wikis and GRC records keep resolving, with view-in-browser plus download in the original format or as PDF.
- Machine-readable from day one: ingestion converts policies to structured, clause-level content, the corpus your RIG assistant and your own enterprise AI agents query over API, permissions travelling with every chunk.
Draft, review, approve, published - automatically.
A guided, step-by-step workflow takes authors from draft through review and approval to publication; publishing is automatic when the last approval lands, with no separate “publish” step to forget. Routes differ by materiality: escalated gates for high-risk policies, accelerated minor updates for typos that don’t reset the review clock.
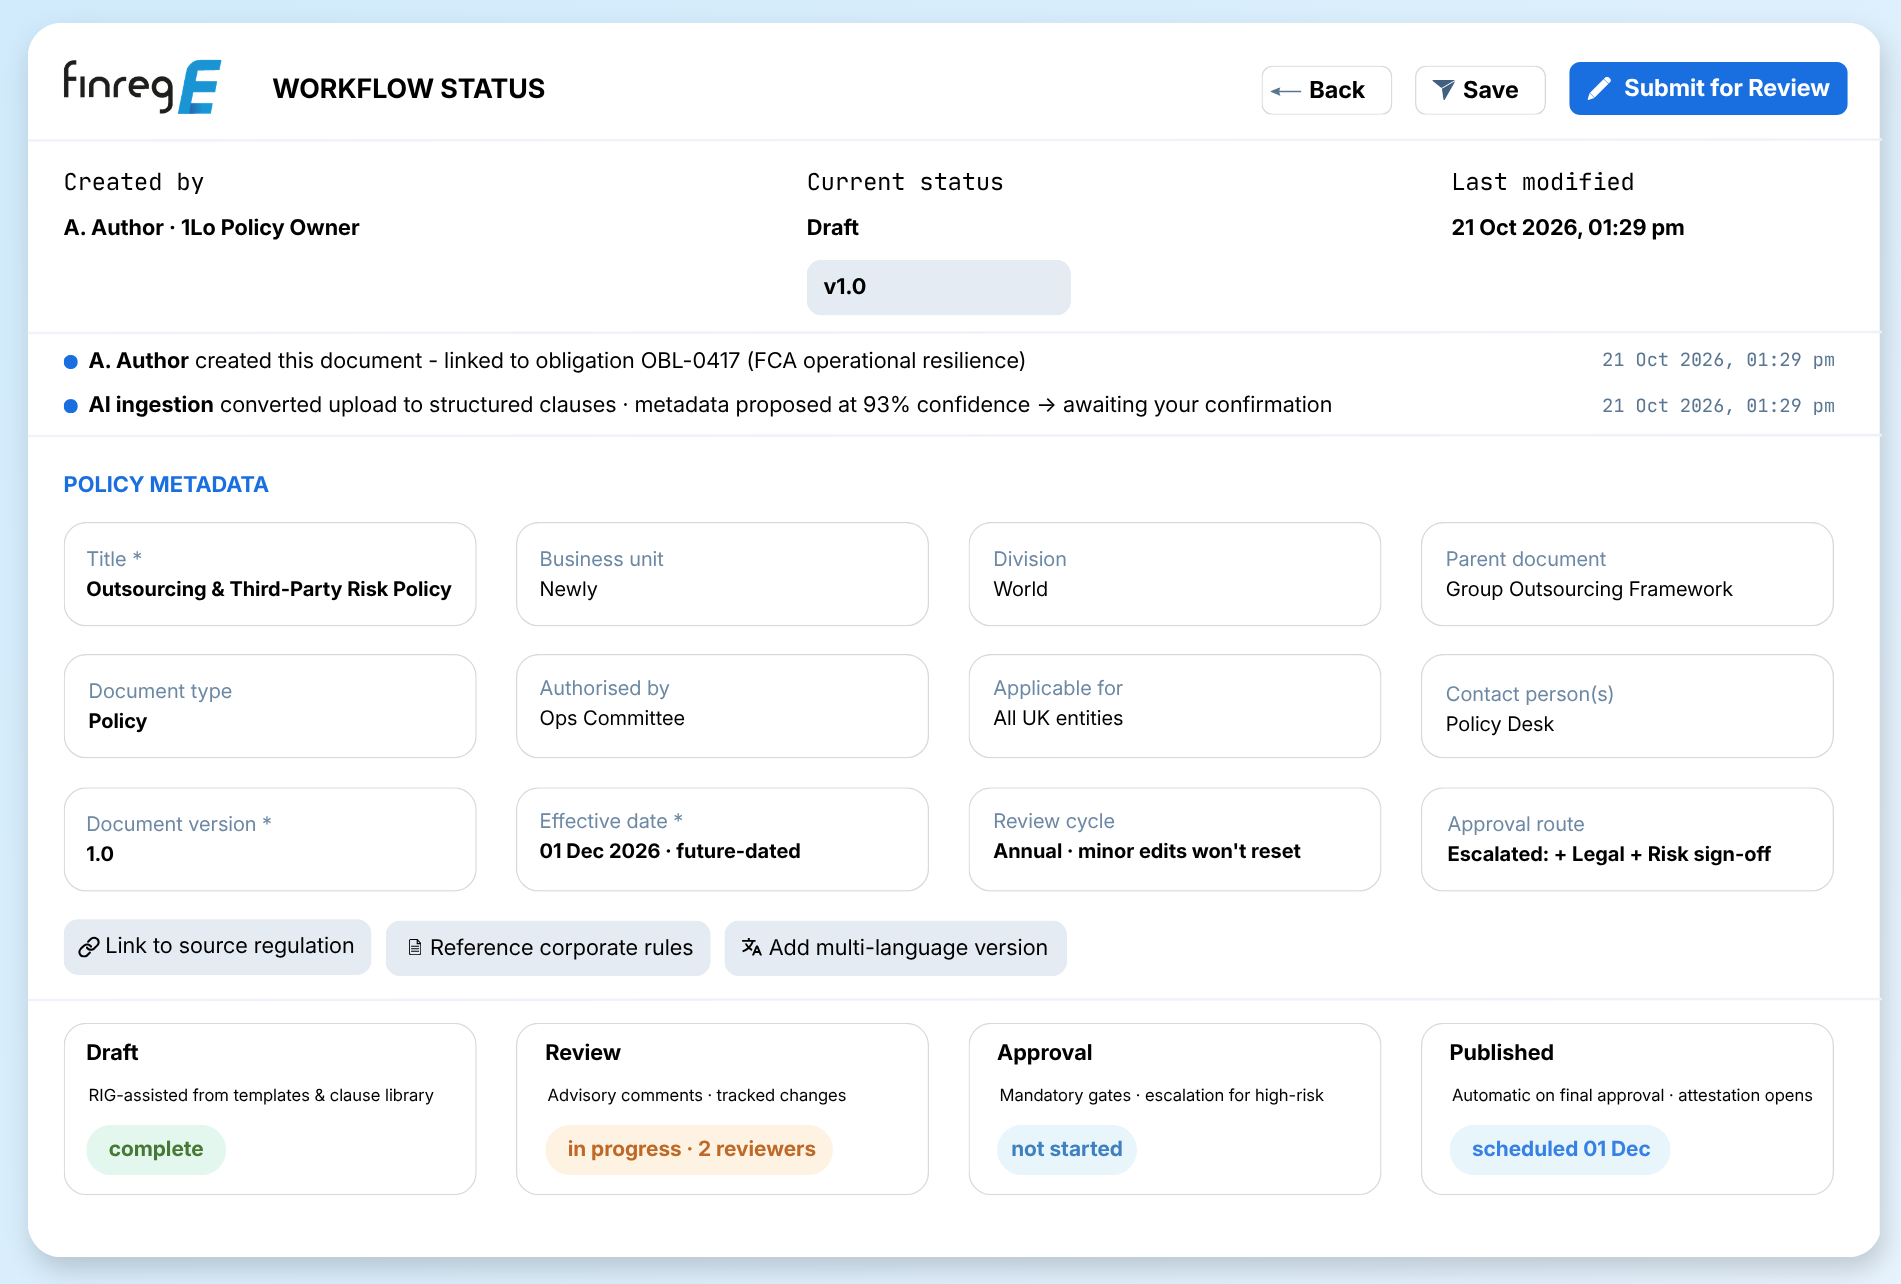
Separate approval routes for material and immaterial changes, with different reviewers, timelines and validation requirements, saved per policy type.
Typo and metadata fixes increment v1.0 >> v1.1 in an accelerated flow while the original expiration and next-review date are preserved.
Executive sign-off, SME review or legal validation inserted per policy type or by risk classification, every escalated step logged.
Bulk-reassign a departing approver’s whole queue in one audited operation; admins can act on an approver’s behalf with both identities recorded.
Accountability you can export.
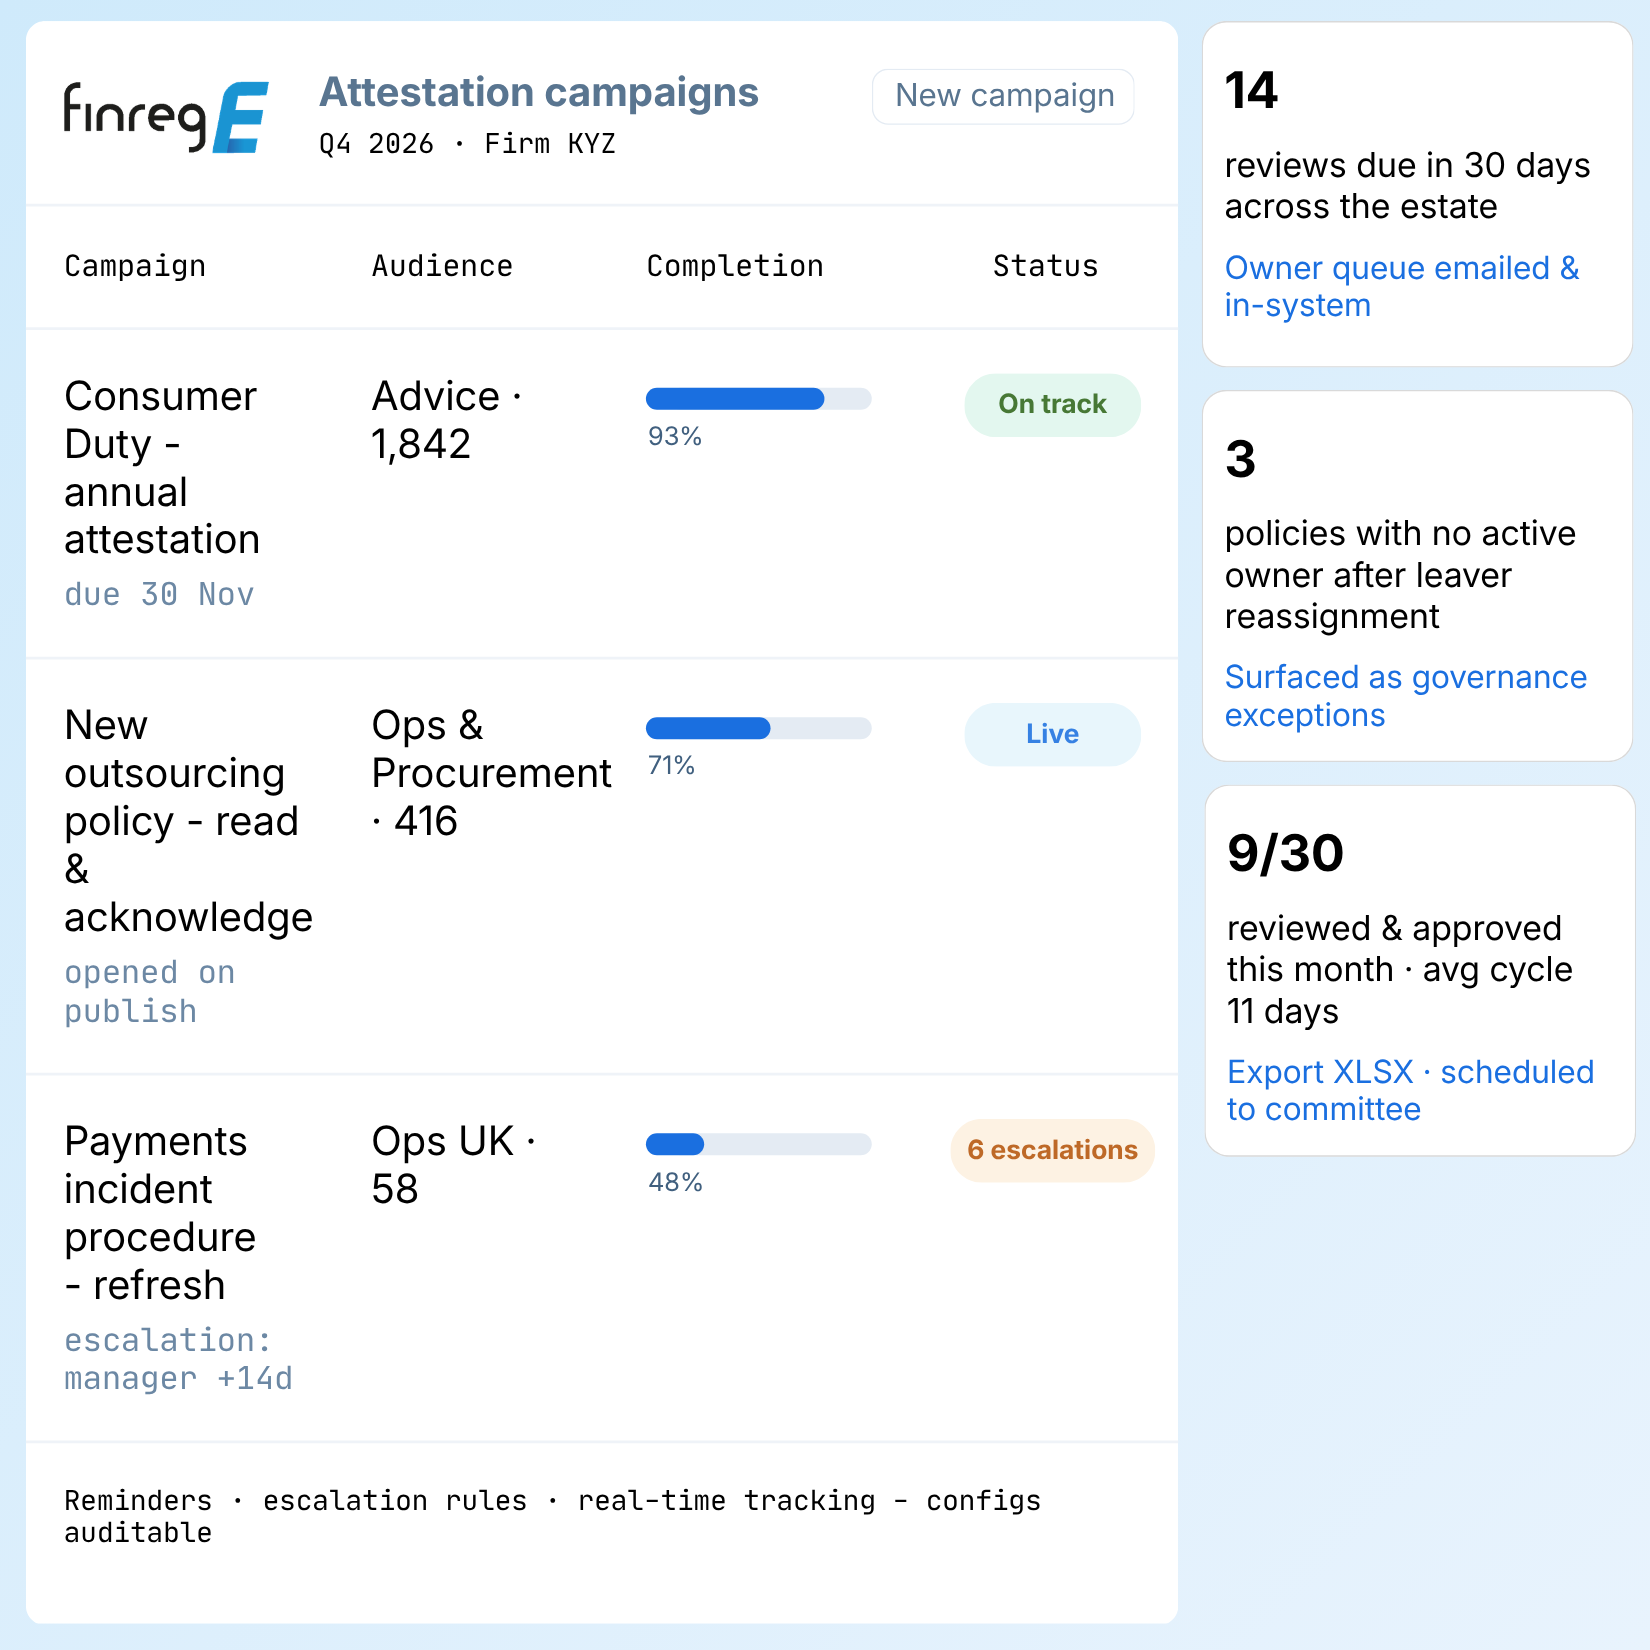
Every policy carries a review cadence; 12 months, 24, custom per type or entity. Expiry and next-review dates calculate automatically; owners get branded email and in-system reminders; overdue work escalates by role. Attestation campaigns confirm people have read what applies to them.
- Attestation campaigns: target populations, schedules, reminders and escalations per campaign, tracked to completion in real time.
- Read & acknowledge on publish: impacted audiences get change summaries with links; acknowledgement progress is measurable, not assumed.
- Role-based dashboards: owners see their due queue; approvers see pending tasks; admins see estate-wide review status, orphaned policies and approval exceptions.
- Scheduled reports & evidence packs: weekly or monthly MI to stakeholder groups (recipients don't need licences); version history, approvals and attestations exported as PDF/XLSX for audit and supervisors.
- Audit trail aligned to versions: every create, edit, approve, reject, publish and retirement logged with user, timestamp and before/after values, retrievable “as at” any date, even for people who left.
Ask. Don't search
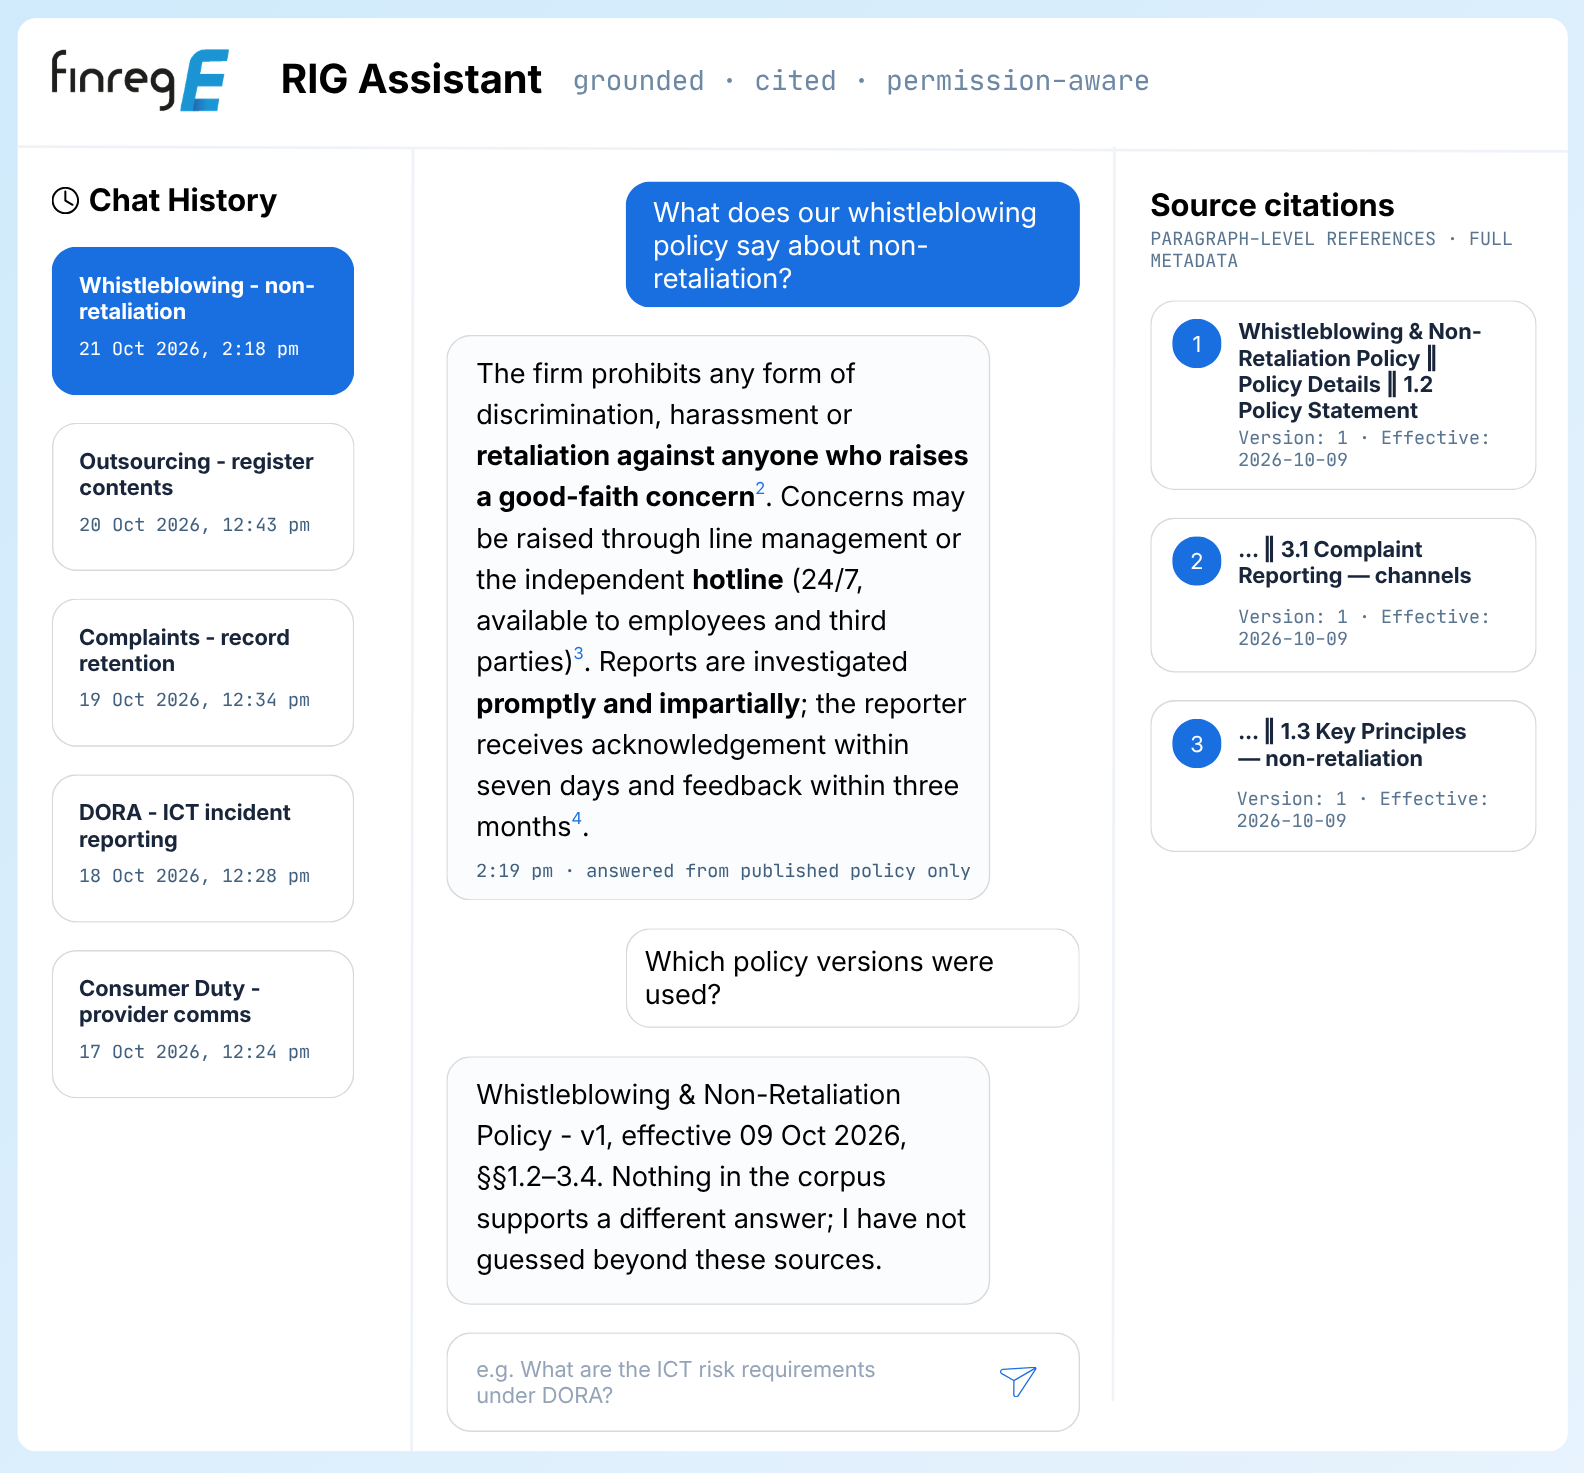
Ask RIG answers natural-language questions about a policy or the whole library, grounded in your published documents, cited to the paragraph, and confined to what the asker is entitled to see. “What does our whistleblowing policy say about non-retaliation?” returns the answer, the basis, and the version it came from.
- Cited, not guessed: every answer links document, section and version in a parallel source panel, check it in one click. If nothing published supports an answer, RIG says so.
- Permissions enforced at query level: if a user can't see HR policies, the assistant can't surface them, RBAC applied to AI input and output, every prompt and response logged.
- Beyond Q&A: audience-tailored change summaries (executive, employee, audit), AI metadata tagging with confidence scores, and drafting checks that flag conflicts with regulation and other policies before publication.
- AI you can take to the risk committee: your data is never used to train external models; inference stays in your Azure region; human sign-off stays mandatory. Production regulatory AI since 2018, not a wrapper.
Prove coverage at clause granularity.
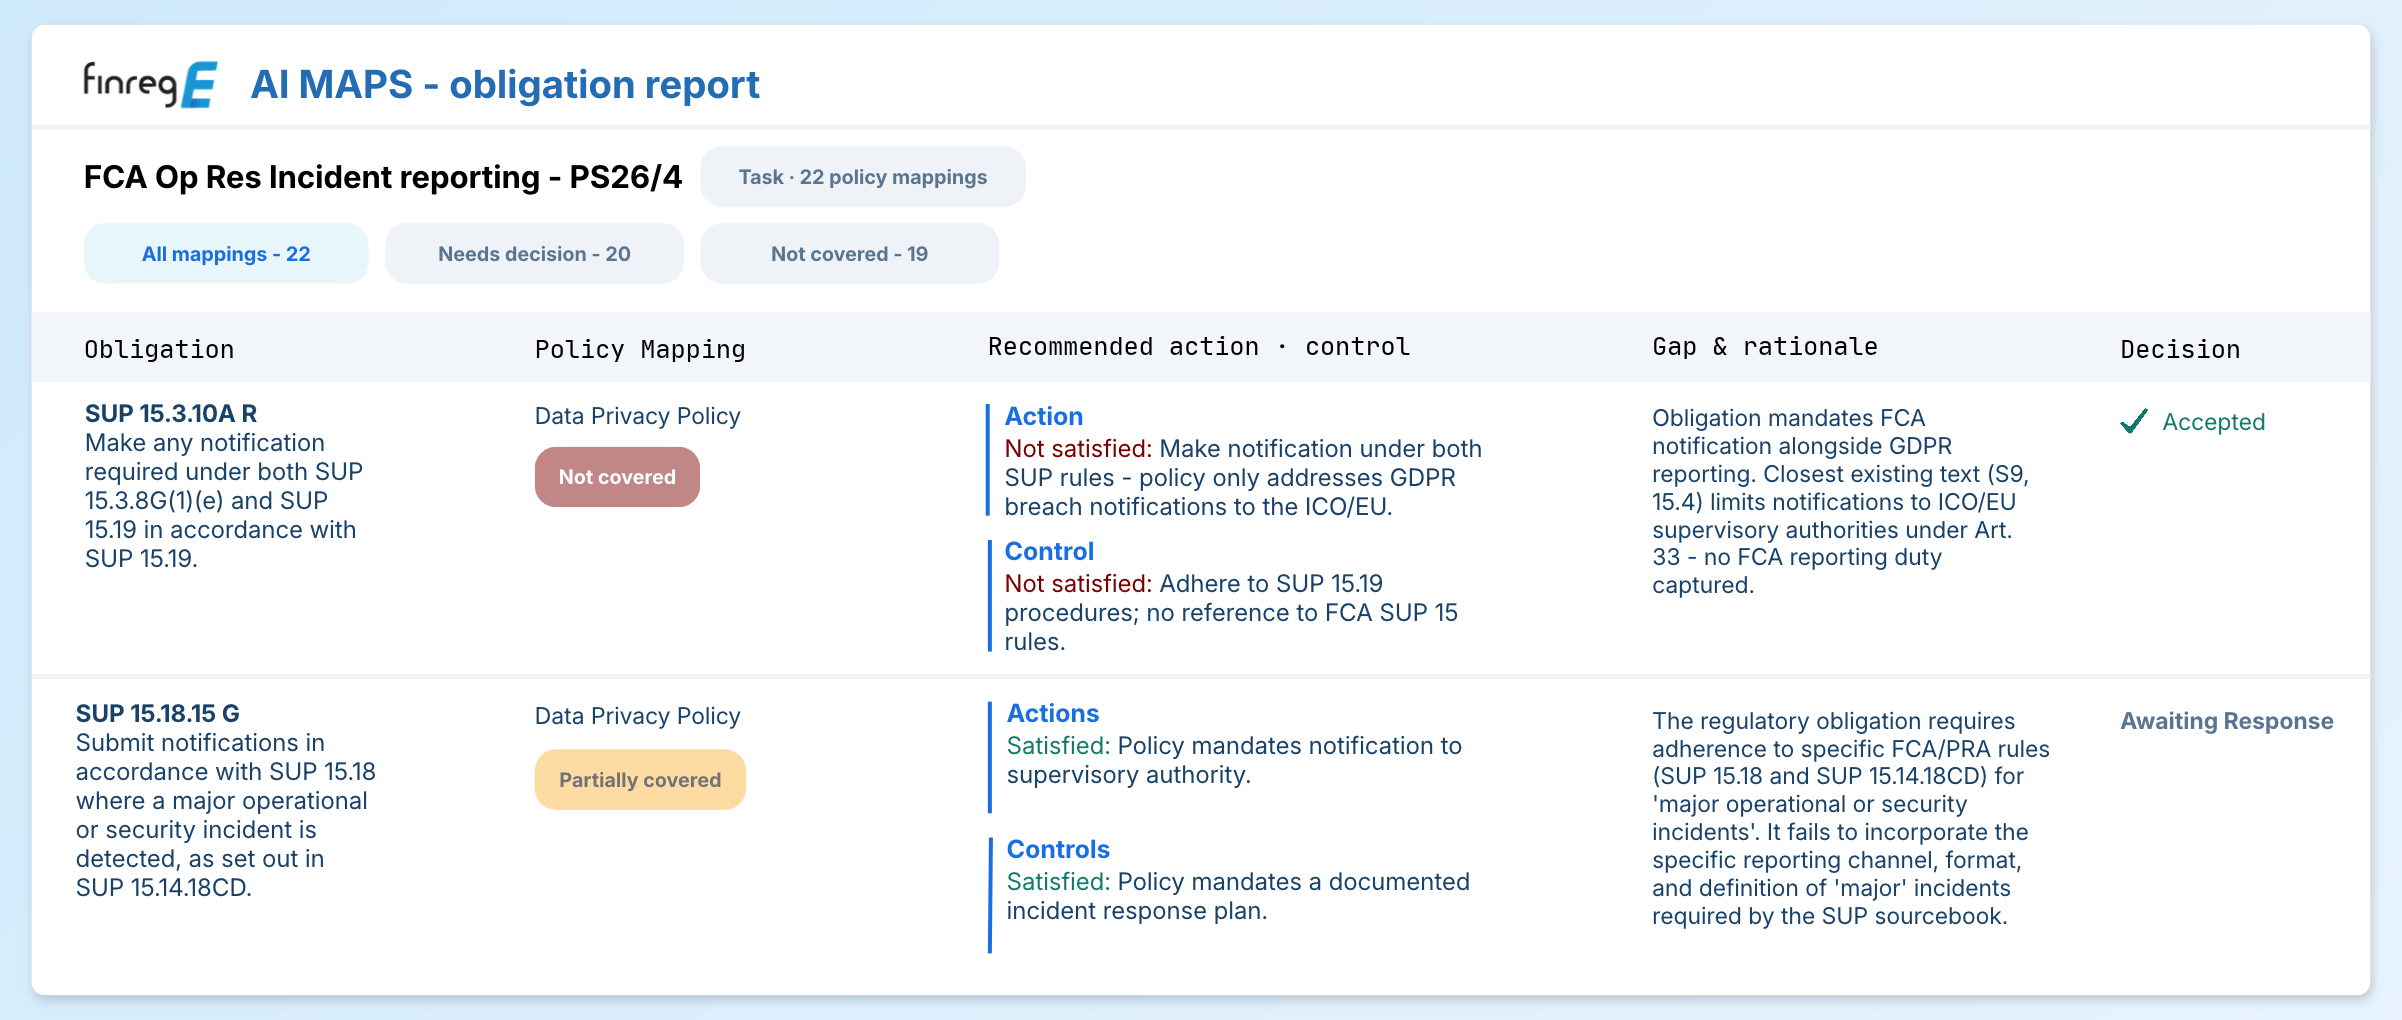
FinregE MAPS analyses applicability and maps regulation to your policies at rule, citation and obligation level, flagging conflicts, duplicates, orphans and unmapped obligations. When a rule changes, mapped policies are surfaced automatically and a governed redraft can open before the deadline, not after the audit.
Bi-directional lineage
From a regulation to the clauses that meet it or from a policy to every obligation it carries. Lineage survives version changes, so “what was this policy based on in March?” has an answer.
Gaps with reasons
Fully covered/ partially covered/ not covered, with the dimension that fails (action, control, specificity, timing…) and an AI-drafted, cited fix you accept or reject. Nothing silently green.
Fed by Horizon Scanning
The same platform monitors 3,000+ regulatory sources in 160+ jurisdictions. A new consultation or final rule highlights affected policies and can open the review automatically.
The answers to the questions every firm we work with asks
Policy platforms hold your firm’s rulebook, the highest-sensitivity internal corpus there is. FinregE was built inside regulated institutions, so the control story is part of the product, not an add-on.
AI governance
- Your content is never used to train external or shared models, contractually, not just by policy
- Answers are cited to source or refused, no unsupported generation on your rulebook
- Human-in-the-loop is structural: AI drafts and flags; only named people approve, and every prompt is logged
- Role-based access is enforced inside AI retrieval, not just in the UI
- Inference runs in your Azure region - UK, EU, NA or APAC data residency
Platform & assurance
- ISO 27001:2022 certified and FSQS assessed; SOC 2 programme in flight
- 99.9% uptime SLA; 99.98% achieved over the last 12 months
- RPO ≤ 15 minutes, RTO ≤ 2 hours; AES-256 at rest, TLS 1.2+ in transit
- 7-year record retention with immutable audit history, including AI interactions
- Azure-hosted, single-tenant per client, SSO via Entra ID, SCIM provisioning, per-client encryption keys
Governance your whole firm can stand on.
Policy owners & SMEs
Draft with AI assistance and live regulatory citations; see exactly which obligations your document carries and what changed since the last version. Track your owned documents and act on review tasks in one queue.
Reviewers & approvers
Approve from a task dashboard with redlines, metadata, mappings and prior decisions side by side. Delegated and parallel approvals keep queues moving when an approver changes roles or leaves.
Policy & process managers
Run review and attestation campaigns on schedules, chase from one MI view, and answer the supervisory question “who approved what, when, on what basis?” without rebuilding the evidence by hand.
Every employee
A searchable, always-current rulebook with AI Q&A, read and acknowledge in the flow of work, at whatever depth their role requires. No more “which version is authoritative?”
Identity & access
Microsoft Entra ID SSO · SCIM provisioning · role-based permissions down to individual documents and AI queries · bulk re-permissioning on org change
Workplace & reporting
Microsoft 365 / SharePoint ingestion & publishing · Teams notifications · Power BI dashboards · Outlook action emails with deep links
GRC & ITSM
ServiceNow · Archer · MetricStream · custom REST APIs and webhooks · S3 / Azure Blob connectors · enterprise AI agents can call your policy library under the same RBAC
Migration & onboarding
We migrate existing policy libraries; Word, SharePoint, GRC exports, preserving metadata, versions and audit history. Typical go-live in 8–12 weeks, training included.
Questions compliance leaders ask us first.
Can our admins configure workflows, roles and templates without calling you?
Yes. Workflow stages, parallel and serial approvals, escalation gates, review frequencies, attestation campaigns, document types, metadata fields and role mappings are all self-service configuration, changed by your administrators in the UI, versioned, and effective immediately for new instances. No professional-services ticket per tweak.
Does a small typo fix restart the whole approval clock?
No. Materiality classification is configurable: immaterial edits (typos, formatting, metadata) can take a fast path; owner-only or single-approval, without resetting the policy’s version cadence or triggering a full re-attestation. Major revisions take the full route. The classification decision is logged either way.
What can bulk operations do and what do they deliberately not do?
Bulk actions cover the reversible, structural things: reassigning approvers when people change roles, moving documents between taxonomies, re-tagging metadata, rescheduling reviews. We deliberately do not offer bulk content edits, changing policy text in bulk would bypass the per-document review that approvals exist to enforce.
Can confidential documents leak into AI answers for people who shouldn't see them?
No, permissions are enforced inside AI retrieval, not just the UI. If a user cannot open a document, it is never in their prompt context, and the assistant is built to refuse rather than improvise when its permitted corpus has no answer. Every prompt, source and response is logged for audit.
How does this connect to Horizon Scanning and Maps?
Horizon captures the regulatory change, RIG assesses impact, and Governance turns it into a governed redraft with the obligation mapping already in place. Maps then shows enterprise-wide coverage of obligations by policy and control, one continuous thread from regulator to clause.
How bad is migration from Word, SharePoint or our current GRC tool?
It’s the part we’ve industrialised. We ingest Word, PDF, SharePoint libraries and GRC exports, preserve metadata, version history and ownership where it exists, and map your taxonomy on import. Typical implementation is 8–12 weeks including training, and you keep your document templates; we don’t force a house format on you.
Is the AI accurate enough to trust with mapping and summaries?
Our extraction and classification models run above 90% measured accuracy on regulatory content, every output is cited to its source, and every AI result sits behind a human accept/reject decision, mapping decisions, redlines and metadata all carry explicit human sign-off with full audit history. Accuracy claims without a human gate are how audits go wrong.